cyber-security
AI’s Double-Edged Impact on Telecom Networks: Accelerating Cyber Threats While Improving Network Resilience
Disclaimer: ChatGPT was used in a dialog to help select this important telecom topic and subsequently conduct research that the author used to write this article.
Introduction:
Artificial intelligence (AI) is creating a fundamental paradox for telecommunications networks and other critical infrastructure. The same technology that enables network operators to predict equipment failures, improve service reliability and detect security threats can also help malicious actors discover software vulnerabilities, develop exploits and accelerate cyberattacks.
AI is therefore becoming both a potential source of increased network risk and an important tool for reducing it. The outcome will depend on how quickly telecommunications providers and other critical infrastructure operators can deploy effective AI-enabled defenses, improve operational resilience and cooperate in responding to emerging threats.
AT&T CEO John Stankey recently highlighted this dilemma at Semafor’s Silicon Valley & The World conference. He said AI makes all companies more vulnerable to cyberattacks, at least for now, but rejected a pessimistic outlook. “At this moment in time, I think everybody’s more vulnerable,” said Stankey. “The meat’s going to be put on the bones by businesses and industry working with each other, working with those that are generating the new technology … and it’s going to require better sharing,” he added.
Stankey believes AI can ultimately make critical infrastructure safer. However, he cautioned that businesses need time, better information sharing and cooperation with AI developers to turn the technology from a liability into an advantage. His comments reflect an increasingly urgent cybersecurity challenge: AI is accelerating both the discovery of vulnerabilities and the ability to exploit them. He highlighted Anthropic’s Project Glasswing controlled rollout as an example of how businesses can work with AI technology companies in assessing security risks and finding vulnerabilities before new AI models are widely released.
“Now there’s a long list of things that have to be addressed and fixed, many of which are going to stretch out for two years or more. The question, how much risk do you want to take during that period, and how do you mitigate that?” Stankey concluded.
AI Increases the Cyber Threat from Malicious Actors:
AI is changing the economics and speed of cyberattacks. Previously, many sophisticated attacks required substantial human expertise and considerable time to identify targets, investigate network weaknesses and develop working exploits. Advanced AI models can increasingly automate or accelerate portions of that process.
Potential applications by malicious actors include:
- Automated reconnaissance: Identifying exposed network infrastructure, vulnerable systems, software versions and misconfigured services.
- Vulnerability discovery: Analyzing large software codebases, firmware and system configurations to identify weaknesses that conventional security tools may overlook.
- Exploit development: Assisting with the development and testing of exploit code and identifying ways to combine multiple vulnerabilities into an effective attack.
- Social engineering: Generating convincing phishing messages, impersonation attempts and other targeted communications.
- Attack orchestration: Using AI agents to automate reconnaissance, target selection and other stages of an attack.
The UK National Cyber Security Centre (NCSC), in its 2026 Annual Review, describes AI as a force multiplier for cyber threats, increasing their scale, speed and efficiency. It identifies reconnaissance, social engineering, vulnerability discovery and exploit development as areas where AI is already changing cyber operations.
Importantly, the NCSC does not conclude that AI has fundamentally changed the objectives of hostile actors or that fully autonomous cyberattacks are commonplace. Rather, AI is expected to accelerate and scale existing attack techniques. Human operators remain important in directing and validating AI-generated results, particularly for sophisticated operations.
The concern is that AI-assisted vulnerability discovery and exploit development could substantially shorten the interval between identifying a weakness and exploiting it. Network operators and software suppliers may have less time to evaluate, patch and remediate vulnerabilities before attackers attempt to use them.
Claude Mythos illustrates the changing threat:
Anthropic’s Claude Mythos Preview provides an important example of the capabilities involved. The model demonstrated advanced abilities to identify software vulnerabilities and construct complex exploit chains. Anthropic subsequently established Project Glasswing, a controlled initiative providing selected technology companies and critical infrastructure organizations with access to the model for defensive security work.
One participant, Comcast, used Claude Mythos Preview to examine 258 business-critical systems encompassing approximately 170 million lines of code. According to Anthropic, the model identified a critical authentication vulnerability in a public-facing platform that existing scanners had missed. The weakness was remediated before evidence of exploitation was observed.
This example demonstrates why AI-enabled vulnerability discovery matters. A weakness that might appear insignificant when examined in isolation can become serious when combined with other software or configuration problems. AI models can help trace these relationships across complex systems.
However, the same capabilities could eventually be used by hostile actors. The defensive advantage provided by controlled access to advanced models is not a permanent guarantee that comparable capabilities will remain unavailable to attackers.
Telecom Operators Use AI to Improve Network Reliability:
The cybersecurity threat is only one side of AI’s impact on telecommunications. Network operators are also applying machine learning, predictive analytics and increasingly agentic AI to improve network operations.
Modern telecommunications networks generate enormous volumes of telemetry, performance measurements, alarms and configuration data. These data originate from routers, switches, optical transport systems, radio access networks, core network equipment, data centers and supporting infrastructure.
Conventional network management systems frequently rely on predefined thresholds, rules and alarm correlation. These methods remain useful, but they can struggle to identify complex failures involving multiple network elements, vendors and interconnected domains.
AI can analyze much larger volumes of operational data, recognize patterns and identify developing problems that might otherwise remain undetected until service performance deteriorates.
1. Detecting incipient network failures
AI-based network analytics can identify anomalies and early warning signals, including:
- Unusual traffic patterns, congestion and increasing packet loss or latency.
- Deteriorating optical link performance and transceiver behavior.
- Abnormal temperature, power consumption or cooling conditions.
- Changes in equipment performance that precede hardware failures.
- Correlated alarms across network elements that may indicate a common underlying problem.
By identifying these conditions earlier, operators can investigate and correct problems before they develop into service-affecting outages.
2. Predictive maintenance
Predictive maintenance applies AI to historical equipment performance, real-time telemetry and failure patterns to estimate the likelihood of future component failures.
For example, an AI system might identify an optical transceiver exhibiting progressive performance degradation, a power supply showing abnormal behavior or a network component approaching a failure condition. Maintenance teams can then schedule inspection or replacement before the component fails.
The potential benefits include fewer unplanned outages, reduced maintenance costs, fewer unnecessary truck rolls and improved network availability.
3. AI-assisted fault isolation and network operations
AI can also correlate alarms, identify probable root causes and recommend corrective actions across multiple network domains. This can reduce the time engineers spend collecting data and manually investigating complex incidents. A concrete example is NTT DOCOMO’s commercial deployment of an agentic AI system for mobile network maintenance in February 2026. Developed using AWS services, the system analyzes traffic and alarm data in real time from more than one million network devices, including base stations and core network equipment.
It uses multiple AI agents and graph-modeled network topology to identify anomalies, locate suspected failure points and recommend actions to maintenance engineers. DOCOMO reported that the system reduced response times for complex network failures requiring manual analysis by more than 50%. This is an important example because the system is not simply generating summaries of network alarms. It is correlating operational data across a large, interconnected network to assist in fault isolation and service restoration.
Nevertheless, DOCOMO’s implementation retains human involvement in evaluating recommended actions. This is an important distinction when AI is being introduced into production networks where an incorrect automated response could cause additional service disruption.
AI Also Strengthens Telecom Cybersecurity Defenses
AI applications in network reliability and AI applications in cybersecurity are different disciplines, but both benefit from the ability to analyze large volumes of data, identify anomalies and recognize relationships that may not be apparent through conventional monitoring.
Telecom operators can use AI-based security systems to:
- Analyze network traffic and security logs to identify suspicious behavior and potential intrusions.
- Detect unusual access patterns, compromised accounts and potentially infected network elements.
- Correlate security events across network infrastructure, cloud environments and enterprise IT systems.
- Identify vulnerabilities in software, firmware, APIs and network configurations.
- Prioritize vulnerabilities based on exposure, exploitability and potential service impact.
- Accelerate security investigations, incident classification and containment.
AI-assisted vulnerability analysis is particularly significant. Conventional vulnerability scanners are useful for identifying known weaknesses and individual coding problems, but may not recognize complex exploit chains involving multiple software components and configuration settings.
As the Comcast example illustrates, advanced AI models can examine relationships across codebases and identify weaknesses that conventional scanning tools may miss.
This creates an opportunity for telecom operators to use advanced AI capabilities to examine their own network software, management systems and supporting infrastructure in ways that more closely resemble how sophisticated attackers might investigate them.
However, identifying a vulnerability is only the beginning. Operators must validate whether it is exploitable in their actual environments, determine its severity, identify affected systems and deploy appropriate remediation without disrupting services.
AI Cybersecurity Arms Race: Can Defenders Keep Pace?
The central question is whether AI-enabled defenses can advance quickly enough to offset the additional capabilities AI provides to attackers. Both sides can benefit from faster vulnerability discovery, automated analysis and improved recognition of complex patterns. But the operational circumstances are different. An attacker may need to identify only one exploitable weakness to compromise a target. A telecommunications provider must protect a complex, continuously operating infrastructure comprising thousands or millions of network elements, multiple vendors, legacy systems, cloud-native functions and interconnected management platforms. Furthermore, operators cannot simply apply every available patch or configuration change immediately. Network changes must be tested, validated and coordinated to avoid introducing service disruptions. In some cases, maintenance windows, equipment compatibility and dependencies among network functions complicate remediation.
This creates several challenges:
- The vulnerability remediation backlog. AI may identify vulnerabilities faster than operators and equipment suppliers can validate, prioritize and correct them. A larger volume of findings does not automatically translate into improved security.
- False positives and exploitability. AI-generated vulnerability reports require technical validation. Not every identified weakness is exploitable, and not every theoretical exploit represents an immediate operational threat.
- The risks of automated remediation. AI systems that recommend or execute network changes must operate within carefully defined permissions and policies. An incorrect configuration change or automated response could cause the very service disruption the operator is trying to prevent.
- AI system security. AI agents themselves introduce new risks involving access permissions, sensitive operational data, model manipulation, unreliable outputs and potentially unauthorized actions. Operators must secure the AI systems used to protect their networks.
- Human oversight. AI can accelerate analysis and decision-making, but network operators remain responsible for service availability, security and regulatory compliance. Human validation and well-defined escalation procedures remain essential, particularly for high-impact network changes.
The challenge is therefore not simply to deploy more AI. It is to integrate AI into operational and cybersecurity processes with sufficient accuracy, governance and accountability to improve resilience rather than create additional vulnerabilities.
Cross-Sector Cooperation Is Essential:
Stankey’s call for greater cooperation recognizes that cybersecurity threats do not respect industry boundaries. Telecommunications networks support financial services, healthcare, transportation, energy, government and virtually every other major economic sector. A compromise affecting one part of this interconnected infrastructure can have consequences well beyond the original target.
Effective defenses therefore require more than individual companies improving their own security operations.
Telecommunications providers, equipment manufacturers, cloud service providers, AI developers, cybersecurity firms and government agencies need to share actionable threat intelligence and coordinate responses to vulnerabilities affecting common infrastructure.
AT&T is a founding member of the Alliance for Critical Infrastructure, which brings together companies from communications, energy, financial services, information technology, transportation and water systems. The initiative provides a forum for cooperation among organizations that have a shared interest in protecting critical infrastructure.
As note above, Anthropic’s Project Glasswing is another example of cross-industry cooperation. By providing selected organizations with access to advanced AI models for defensive security research, the initiative seeks to identify and remediate vulnerabilities in critical software before comparable capabilities become more widely available. Such initiatives are useful, but cooperation must translate into operational results: faster vulnerability disclosure, coordinated patch development, improved threat intelligence sharing and more effective incident response.
Conclusions: AI Can Make Telecom Networks More Resilient, but Not Automatically More Secure:
AI is simultaneously increasing the cyber threat and providing telecommunications providers with new tools to improve network reliability and security. Malicious actors can use AI to accelerate reconnaissance, discover vulnerabilities, develop exploits and scale existing attack techniques. Telecom operators, meanwhile, can use AI to detect incipient network failures, predict equipment degradation, improve maintenance, identify security anomalies and accelerate vulnerability remediation. These applications should not be confused. Predicting an optical transceiver failure is fundamentally different from detecting an intrusion or identifying an exploitable software vulnerability. Nevertheless, both demonstrate AI’s ability to extract actionable intelligence from enormous volumes of complex network data.
The DOCOMO deployment illustrates the operational benefits already being achieved through AI-assisted fault isolation. Anthropic’s Project Glasswing and Comcast’s experience demonstrate how advanced AI models can help defenders identify security weaknesses that conventional tools may miss. Neither example, however, establishes that AI can independently guarantee network reliability or cybersecurity.
The ultimate issue is whether defenders can use AI more effectively than attackers can use it to exploit weaknesses. That will require continuous vulnerability assessment, faster remediation, secure AI deployment, rigorous operational controls and cooperation across critical infrastructure sectors. Repositioning AI from a cybersecurity liability into a defensive advantage will require more than adopting new models and automation tools. It will require telecom operators and their partners to fundamentally improve the speed, coordination and effectiveness of network operations and security.
…………………………………………………………………………………………………………………………………………………………………………………………..
References:
https://www.semafor.com/hub/semafor-silicon-valley-and-the-world-2026
https://www.ncsc.gov.uk/collection/annual-review-2026/understanding-threat/ai-impact-cyber-threat
https://www.ncsc.gov.uk/sites/default/files/2026-11/ncsc-annual-review-2026.pdf
https://www.anthropic.com/project/glasswing
https://dcm-dpweb61.tz.nttdocomo.co.jp/english/info/media_center/pr/2026/0225_01.html
https://www.nokia.com/blog/from-prediction-to-action-the-next-leap-in-ai-driven-network-care/
Gates warns of “turbulent AI era;” OpenAI calls for collective action on AI cybersecurity
Anthropic’s Project Glasswing aims to reshape IT cybersecurity
SHIELD-6G with AI-native cyber threat intelligence platform to enhance cybersecurity for Europe’s future 6G networks
Cybersecurity threats in telecoms require protection of network infrastructure and availability
Analysis & Implications of the Communications Cybersecurity Information Sharing and Analysis Center (C2 ISAC)
Key Differences Between Network Cybersecurity and Control System Cybersecurity & Why It Matters
Emerging Cybersecurity Risks in Modern Manufacturing Factory Networks
StrandConsult Analysis: European Commission second 5G Cybersecurity Toolbox report
Palo Alto Networks: Frontier AI Critical Defense Program + Collaboration with NTT DATA for secure AI adoption
Palo Alto Networks Introduces Frontier AI Critical Defense Program:
Yesterday, cybersecurity leader Palo Alto Networks joined Nvidia and Anthropic in assembling a high-profile coalition focused on defending critical infrastructure against AI-enabled cyberattacks.
Gartner defines AI in cybersecurity as: “The application of AI technologies and techniques to enhance the security of computer systems, networks, and data to protect from potential threats and attacks. AI enables cybersecurity systems to analyze vast amounts of data, identify patterns, detect anomalies, and make intelligent decisions in real time to prevent, detect, and respond to cyberthreats.”
Using AI in cybersecurity solutions leads to faster and more accurate threat detection along with greater scalability and cost efficiencies. Palo Alto Network’s Frontier AI Critical Defense Program expands on its existing collaborations with IBM, Red Hat, Microsoft, Siemens, and Idaho National Laboratory. Anthropic, OpenAI, and Mitsubishi have now joined the initiative, which is focused on protecting operational technology (OT), health-care systems, commercial software, and open-source ecosystems from AI-driven exploits.
Participating organizations will work with Palo Alto Networks to identify and mitigate vulnerabilities at network scale. One element of the program is the deployment of “virtual patches”—network-level controls designed to neutralize known or newly discovered security weaknesses before software fixes can be developed, tested, and widely deployed.
Palo Alto Networks said its work with compute-intensive frontier AI models has already identified more than 14,000 previously unknown vulnerabilities in open-source software. By comparison, Anthropic reported that its Claude Mythos Preview Model had uncovered more than 23,000 flaws across more than 1,000 open-source projects.
IBM and Red Hat’s related Project Lightwell has not yet disclosed comparable findings. However, the initiative remains in its early stages, making direct comparisons premature.
These efforts reflect a broader shift in the cybersecurity threat landscape. AI systems can automate reconnaissance and exploit development while compressing attack timelines from weeks or days to minutes or seconds. Palo Alto Networks describes the objective of its Frontier AI Critical Defense Program as enabling critical infrastructure operators to “patch at ID speed”—that is, at the speed at which vulnerabilities can be identified—thereby narrowing the exposure window between discovery and remediation.
The emerging model represents a transition from predominantly human-paced cybersecurity operations toward a more compute-intensive and increasingly autonomous approach. AI agents can continuously search for vulnerabilities across complex software and network environments, potentially identifying weaknesses before they are discovered and exploited by adversaries using similar technologies.
“In the age of frontier AI, the traditional, reactive race to build and deploy software patches before adversaries exploit a flaw is a losing battle,” Palo Alto Networks Chief Product Officer Lee Klarich explained. “Protecting critical infrastructure requires a structural shift from isolated patching to collective, proactive intelligence. Through initiatives like our Frontier AI Critical Defense Program, we can neutralize threats at the network layer before they are weaponized.”
………………………………………………………………………………………………………………………………………………………………………………
NTT DATA and Palo Alto Networks Form Strategic Alliance to Accelerate Secure AI Adoption:
Today, NTT DATA, a global provider of AI, digital business, and technology services, and Palo Alto Networks have announced a multiyear strategic alliance aimed at helping organizations adopt AI securely, modernize cybersecurity operations, simplify complex technology environments, and strengthen cyber resilience for the AI era.
The agreement represents Palo Alto Networks’ first strategic alliance of this type with a global systems integrator. The companies expect the partnership to generate up to $1 billion in joint business by the end of the three-year period in 2029. The alliance combines Palo Alto Networks’ AI-powered cybersecurity platforms with NTT DATA’s consulting, systems engineering, and managed services capabilities.
Through joint engineering, co-innovation, and coordinated global delivery, the companies will help customers assess cyber risk, deploy AI securely, and continuously optimize their security environments. The resulting solutions are intended to provide an integrated path from cybersecurity strategy and implementation through ongoing managed operations.
Building on the companies’ existing collaboration through the Frontier AI initiative, the alliance will combine Palo Alto Networks’ Unit 42® threat intelligence with NTT DATA’s global cybersecurity expertise, AI-governance capabilities, and managed services. The effort will be supported by joint investments, more than 2,000 certified professionals, and dedicated Forward Deployed Engineers.
Direct engineering collaboration will also give NTT DATA early access to new Palo Alto Networks platform features, enabling the systems integrator to accelerate the development and delivery of AI-security services. The companies initially will focus on highly regulated and critical industries, including financial services, health care, manufacturing, and the public sector.
The initial portfolio will address six strategic transformation areas:
-
Autonomous security operations centers (SOCs): Modernize security operations through agentic AI and managed services that help organizations detect, investigate, and respond to increasingly sophisticated, machine-speed threats while reducing operational complexity.
-
AI governance: Integrate governance, security, and risk management across the AI lifecycle, enabling organizations to address emerging risks and scale AI initiatives with greater accountability, transparency, and control.
-
Identity security: Protect human, machine, and AI-agent identities—including workloads and devices—through an identity-security framework designed to discover, manage, secure, and govern identities across the enterprise.
-
Zero Trust and SASE: Secure users, applications, and data across an increasingly distributed attack surface through a unified Zero Trust and secure-access service edge architecture that incorporates AI-driven threat detection and prevention.
-
Resilient cloud: Improve visibility, compliance, and autonomous risk reduction across multicloud environments through AI-enabled security-posture management and stronger governance.
-
Firewall modernization: Modernize firewall infrastructures to reduce operational complexity, improve visibility, and strengthen enterprise-wide security.
“AI is reshaping both business and cybersecurity, making deep ecosystem collaboration more important than ever,” said Nikesh Arora, Chairman and Chief Executive Officer, Palo Alto Networks. “Expanding our alliance with NTT DATA allows us to operationalize platformization at true global scale, helping enterprises eliminate legacy complexity and move fast without sacrificing safety.” “AI is redefining every aspect of the enterprise, but it is also transforming the threat landscape at unprecedented speed. Organizations need a new approach to cyber resilience that combines AI-driven security, deep industry expertise and global scale,” said Abhijit Dubey, Chief Executive Officer and Chief AI Officer, NTT DATA, Inc.
“Together with Palo Alto Networks, we’re bringing AI-powered cybersecurity innovation together with NTT DATA’s consulting, engineering and managed services capabilities to help clients securely accelerate AI adoption and stay ahead of evolving threats.”
NTT DATA brings world-class cybersecurity expertise to the collaboration, backed by over 7,500 cybersecurity professionals, 70+ delivery centers and 20+ Autonomous Cyber Defense Centers. Paired with Palo Alto Networks AI-powered platforms and Unit 42 threat intelligence, the alliance delivers the technology, expertise and global reach enterprise organizations need to securely deploy AI across complex environments.
About NTT DATA:
Fortune Global 100. We are committed to accelerating client success and positively impacting society through responsible innovation. We are one of the world’s leading AI and digital infrastructure providers, with unmatched capabilities in enterprise-scale AI, cloud, security, connectivity, data centers and application services. Our consulting and industry solutions help organizations and society move confidently and sustainably into the digital future. As a Global Top Employer, we have experts in more than 70 countries. We also offer clients access to a robust ecosystem of innovation centers as well as established and start-up partners. NTT DATA is part of NTT Group, which invests over $3 billion each year in R&D. Visit us at nttdata.com
About Palo Alto Networks:
Palo Alto Networks (NASDAQ: PANW), the global AI cybersecurity leader, protects our digital way of life with a comprehensive portfolio of cybersecurity solutions and platforms across Network, Cloud, Security Operations, AI and Identity. Trusted by 70,000+ customers and powered by Unit 42 threat intelligence, our AI-driven platforms eliminate complexity, empowering enterprises to modernize with confidence and securing the speed of innovation. Explore the future of security at www.paloaltonetworks.com.
………………………………………………………………………………………………………………………………………………………………………………………………
References:
Anthropic’s Project Glasswing aims to reshape IT cybersecurity
Palo Alto Networks and Google Cloud expand partnership with advanced AI infrastructure and cloud security
Highlights and Analysis of July 30th U.S. Senate hearing on AI and telecommunications
Applying Zero Trust at the Wireless Edge: Securing Mixed WPA2 and WPA3 IoT Fleets
Fortinet and Palo Alto Networks are leaders in Gartner Magic Quadrant for Network Firewalls
Key Differences Between Network Cybersecurity and Control System Cybersecurity & Why It Matters
SHIELD-6G with AI-native cyber threat intelligence platform to enhance cybersecurity for Europe’s future 6G networks
Countdown to Q-day: How modern-day Quantum and AI collusion could lead to The Death of Encryption
Cybersecurity threats in telecoms require protection of network infrastructure and availability
Network X Americas: AT&T and Comcast reveal huge AI impact on network operations
Sovereign AI infrastructure for telecom companies: implementation and challenges
Applying Zero Trust at the Wireless Edge: Securing Mixed WPA2 and WPA3 IoT Fleets
By Iftikhar Javed khan with Ajay Lotan Thakur
Abstract
Zero-trust architecture is a security model that eliminates implicit trust based on network location and instead requires every access request to be continuously authenticated, authorized, and validated before it is granted (NIST SP 800-207), Yet while zero-trust architecture is intentionally network-agnostic, practitioners still need concrete design patterns to apply its principles at the wireless edge. This challenge is acute in IoT deployments that span multiple hardware generations, where newer devices support WPA3 while legacy endpoints remain limited to WPA2 and may be unable to support 802.1X supplicants, certificate-based authentication, or endpoint posture agents.
Based on an anonymized critical-infrastructure sensor deployment, this article presents a control pattern that segments devices according to their maximum supported security capability rather than forcing the entire fleet into a single compatibility-mode WLAN. WPA3-capable devices are placed in a WPA3-enforced domain, while WPA2-only devices are confined to a tightly restricted legacy domain.
The pattern combines five controls: capability-aware wireless segmentation, per-device Multi-Pre-Shared Key credentials, least-privilege policy enforcement, RF-exposure reduction, and access-point-integrated wireless intrusion detection. The central argument is that WPA3 is an important wireless security control, but it is not, by itself, a zero-trust architecture. Instead, the article shows how zero-trust principles can be translated into practical controls for networks that cannot immediately replace every legacy endpoint.
The Core Principle: Capability Dictates Posture, Not the Reverse
Most wireless security design begins with a chosen standard and then asks how to make the device fleet conform to it. In a homogeneous estate that works. In a mixed-generation IoT fleet it fails, because the fleet contains devices that physically cannot meet modern baseline sensors that support only WPA2-Personal, cannot run an 802.1X supplicant, and cannot host a posture agent. When a single standard is imposed on such a fleet, one of two things happens: either the network is dragged down to the capability of its weakest device, or the weakest devices are quietly excluded and left unmanaged. Neither is zero trust.
The inversion this article argues for is simple: let each device’s maximum supported security capability determine which policy domain it belongs to, and architect the network around that reality rather than against it. A WPA3-capable sensor and a WPA2-only sensor are not two configurations of the same policy; they are two different risk profiles that deserve two different domains. Once capability is treated as the independent variable, the rest of the design segmentation, credentialing, least-privilege enforcement, RF exposure, and monitoring follows from it.
Step One Is Always Visibility
Before any of this can be designed, the fleet has to be seen. In practice, the first problem in a mixed-capability wireless estate is not choosing controls, it is not knowing, with confidence, what is actually associated with the network and what each device can support. A design built on assumptions about the fleet is a design built on sand.
Visibility therefore comes first, and it has two parts as shown in figure 1. The first is a wireless inventory: enumerating the devices present on the medium, their association state, their supported security modes (WPA2-only versus WPA3-capable, SAE support, Protected Management Frames), and their physical distribution. The second is monitoring the medium itself for what should not be access points and clients that are not part of the sanctioned fleet. Only once the estate is known can devices be grouped by capability and confined to the right domain; and only once the medium is continuously observed can the segmentation be trusted to hold over time.
This reframes the usual order of operations. Segmentation and credentialing are what most WLAN-security discussions start with, but they are the second move. The first move is establishing and maintaining an accurate inventory because you cannot correctly assign a device to a capability domain that you have not yet discovered, and you cannot detect a rogue or misclassified device without ongoing observation.
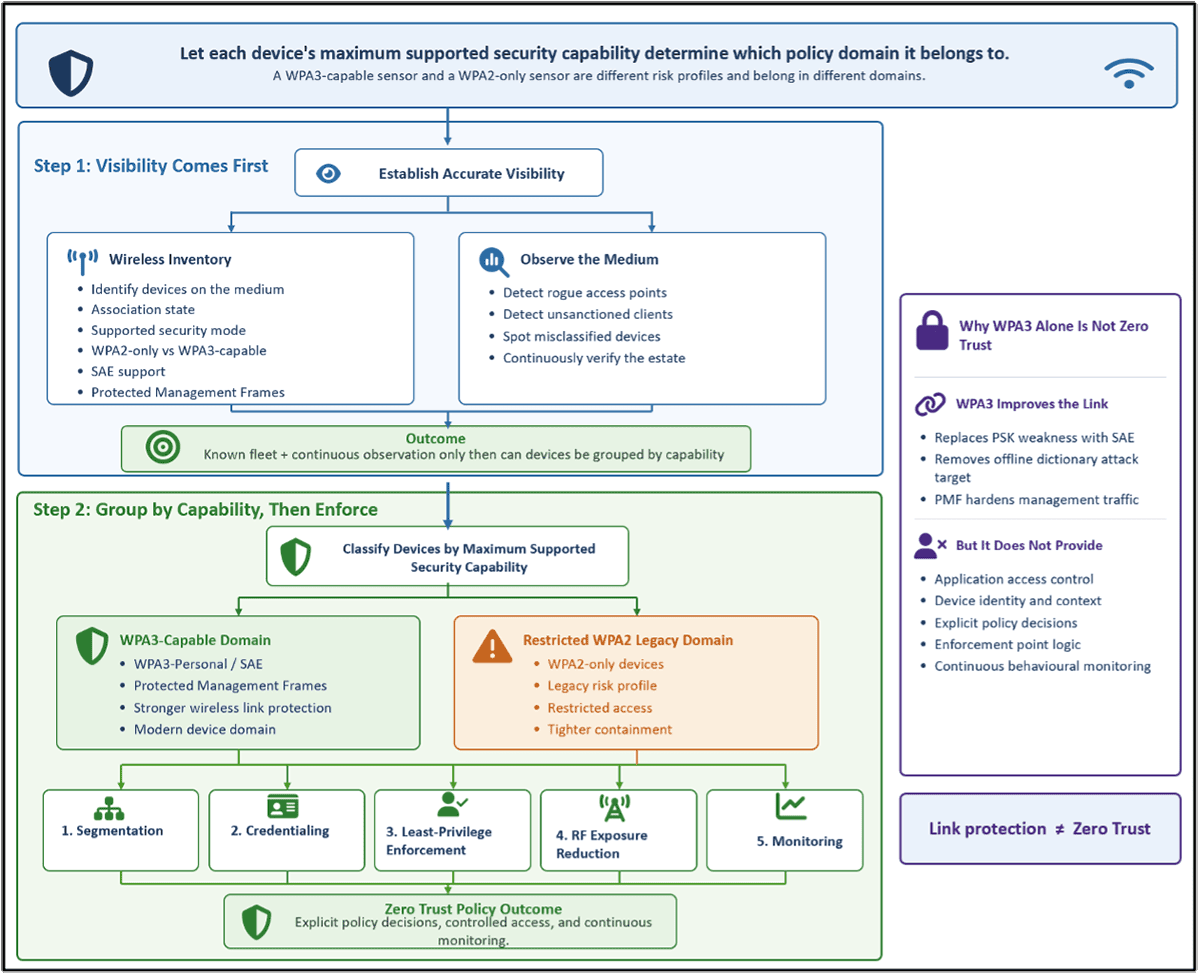
Figure 1: Visibility
Why WPA3 Alone Is Not Zero Trust
WPA3 materially improves the wireless link. Under WPA2-Personal the pairwise master key is derived directly from the passphrase, so an attacker who captures the 4-way handshake can mount an offline dictionary attack against it. WPA3-Personal replaces that PSK authentication with Simultaneous Authentication of Equals (SAE), a password-authenticated key agreement that establishes the pairwise master key without exposing a crackable value the 4-way handshake still runs afterwards to derive and install session keys, but it no longer leaks an offline-attackable target. Protected Management Frames additionally harden management traffic against deauthentication and disassociation abuse. These are real gains, and WPA3-capable devices should use them.
But link protection is not access control. Whether a sensor is on WPA2 or WPA3 says nothing about which application it may reach, whether it may talk to its neighbours, whether it can reach a management interface, or how anomalous behaviour is detected after it has associated. A device can hold a perfectly valid WPA3 credential and still be a compromised endpoint. Zero trust asks a different set of questions than “is the link encrypted”: what is this device, what is it allowed to do, and is it still behaving as expected. Answering those requires credential context, an explicit policy decision, an enforcement point, and continuous monitoring none of which WPA3 provides on its own.

Figure 2: Controls
Control 1 : Capability-Aware Wireless Segmentation
Devices are grouped by their maximum supported wireless security capability and assigned to distinct SSIDs and security zones accordingly: WPA3-capable sensors to a WPA3-enforced domain, WPA2-only devices to a separate, narrowly scoped legacy domain, each with its own firewall and access-control policy.
It is worth being precise about the alternative, because the single-SSID case is often overstated. A WPA2/WPA3 transition-mode SSID is technically possible and would preserve legacy compatibility. The problem is not that one SSID mechanically forces one shared WPA2 key; it is that a transition-mode SSID cannot enforce WPA3-only operation for capable devices, and it places endpoints with materially different risk profiles inside the same wireless policy domain. Separating by capability is a deliberate choice for policy separation and to prevent silent downgrade of capable devices, not a workaround for a technical impossibility. The SSID is not the security boundary; it is the first sorting step, with real enforcement occurring downstream at the firewall or microsegmentation gateway.
Control 2: Per-Device Credential Granularity
A single fleet-wide pre-shared key is replaced with a per-device or narrowly-scoped-group credential scheme, so that a compromised credential exposes one device or a small group rather than the entire fleet, and any one device can be revoked without re-keying everything.
The security benefit is credential granularity and accountability, not cryptographic identity. A pre-shared key remains a possession-based secret: holding it proves possession, not verified device identity, and device identity should never rest on a spoofable MAC address alone. The honest framing is that per-device keying shrinks blast radius and enables granular revocation and gradual rotation, a meaningful improvement over a shared key, but a step below certificate-based authentication, which constrained legacy sensors often cannot support. That gap is precisely why the surrounding controls (segmentation, least-privilege enforcement, monitoring) carry the rest of the load.
Control 3: Least-Privilege Policy Enforcement
This is the control that turns WLAN hardening into a zero-trust pattern, and it is the one most often missing. Each sensor is permitted to reach only the services its function requires, enforced downstream of the wireless layer at a firewall or microsegmentation gateway:
- Permitted: its designated telemetry collector, an authorized DNS resolver, an approved NTP source, and a required update service where applicable.
- Denied: general internet access, sensor-to-sensor communication, any access to wireless or infrastructure management interfaces, and any reach into user, server, or administrative networks.
- Logged: denied flows and policy violations, forwarded to central monitoring for correlation.
Stated plainly: a sensor should be able to send its readings to exactly one collector, resolve names, keep time, and nothing else. Segmentation decides which domain a device lives in; this layer decides what it is allowed to do once there. Without it, capability-aware SSIDs are just better-organized flat networks.
Control 4 : RF-Exposure Reduction
Because the exposure boundary of a wireless network is defined by radio propagation rather than by cabling, access-point placement, transmit power, and minimum data rates are optimized to reduce unnecessary signal propagation beyond the intended service area, validated through an RF survey rather than controller settings alone.
This is defense-in-depth, not a perimeter. RF exposure reduction lowers casual reachability, but a sensitive receiver or a directional antenna can still detect a usable signal outside the intended area, so it must never be presented as containment. Any power or rate change must also preserve required coverage, client uplink performance, roaming behaviour, redundancy, and application reliability; an over-aggressive reduction that breaks associations trades a small exposure gain for an availability loss.
Control 5 : Wireless Intrusion Detection and Continuous Monitoring
Continuous observation of the medium closes the loop opened by the visibility-first principle. Access-point-integrated WIDS/WIPS, or dedicated monitor-mode sensors, observe the over-the-air environment for conditions that IP-layer inspection cannot see, because rogue-AP and evil-twin detection depends on access to raw 802.11 management and control frames rather than post-association traffic.
A practical detection methodology for this environment prioritizes, in order:
- Rogue-AP identification: Unsanctioned access points advertising reachable SSIDs, the highest-priority wireless threat because it can bypass the entire wired policy stack.
- Evil-twin / SSID impersonation: Access points spoofing a legitimate SSID to lure client associations.
- Unauthorized or misclassified clients: Devices associating outside their expected capability domain, or appearing where the inventory says they should not be.
- Association and authentication anomalies: Repeated authentication failures, unexpected device appearance or movement, and deauthentication patterns consistent with over-the-air attack.
Wireless events are forwarded to a central monitoring or SIEM platform and correlated with firewall, authentication, and telemetry logs, so an over-the-air anomaly and a policy violation on the same device can be seen together. Where a network IDS is also used, its role is post-association IP-traffic inspection a separate function from over-the-air 802.11 monitoring, and the two should not be conflated
Reference Architecture
The controls compose into a single flow: capability determines domain, credential and policy determine access, and the medium is continuously observed.
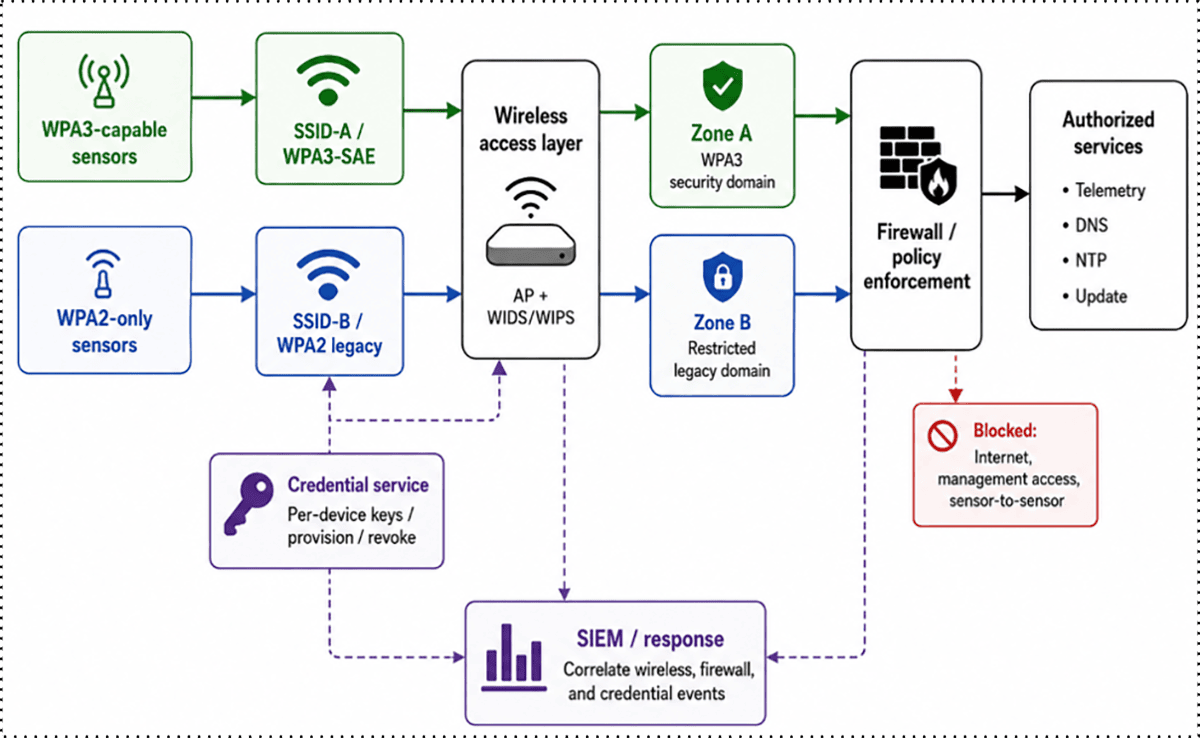
Figure 3: Reference Architecture
Mapping Wireless Properties to Zero-Trust Principles
| Wireless Property | Control Applied | Zero-Trust Principle |
| Heterogeneous device capability | Capability-aware segmentation | Group by risk; do not downgrade capable devices. |
| Shared credential / broad blast radius | Per-device credential granularity | Bounded compromise; granular revocation. |
| Implicit post-association trust | Least-privilege policy enforcement | Explicit per-device authorization. |
| Propagation-defined exposure | RF-exposure reduction | Reduce reachable attack surface (defense-in-depth). |
| Unobserved medium | Visibility + WIDS/WIPS | Assume breach; continuous over-the-air monitoring. |
Applicability to Other IoT Environments
Although derived from a remote environmental-monitoring fleet, the pattern generalizes to any heterogeneous wireless estate that cannot hold every device to one standard healthcare and medical IoT combining modern and legacy or safety devices, building-management and facilities systems, industrial and operational-technology sensors, and smart-city or asset-tracking deployments acquired across long procurement cycles. In each, the same five questions apply, and in the same order: is the estate actually visible; can endpoints be separated by capability and risk; can credentials be scoped per device or small group; can access be restricted to explicitly authorized services; and is the wireless medium continuously monitored.
Limitations and Residual Risks
- WPA2-only legacy devices remain a residual risk until lifecycle replacement; the pattern bounds that risk, it does not eliminate it.
- Per-device pre-shared keys improve granularity but do not provide the assurance of certificate-based authentication.
- RF-exposure reduction lowers casual reachability but cannot prevent reception by sensitive or directional equipment.
- WIDS/WIPS provides detection, not guaranteed prevention; false positives require tuning and operational handling.
- Posture assessment is often limited on constrained endpoints, which is why segmentation and least-privilege enforcement carry more of the load.
- Long-term remediation should include lifecycle planning to retire devices that cannot meet the required security baseline.
Implications for Standards and Practice
As IoT-specific zero-trust guidance matures, the wireless access layer where many IoT deployments are, in practice, most exposed deserves treatment as a primary zero-trust surface rather than a downstream detail. The pattern here is deliberately buildable with widely available capabilities (WPA3/SAE, per-device keying, firewall or microsegmentation policy, AP-integrated WIDS/WIPS), which matters for constrained, hard-to-patch fleets that cannot absorb heavyweight agents. Recent research on trust-boundary management in heterogeneous, multi-radio IoT environments makes a compatible argument that current zero-trust frameworks assume relatively stable networks and under-address dynamic wireless conditions and points to the same conclusion: shared-medium risk, capability-aware segmentation, and wireless monitoring belong in IoT zero-trust frameworks as first-class concerns.
Conclusions
Mixed-capability wireless IoT fleets should not be collapsed into one lowest-common-denominator policy. The more robust approach inverts the usual order: let each device’s capability dictate its security domain, establish and maintain visibility of the medium first, and then apply capability-aware segmentation, per-device credentialing, least-privilege enforcement, RF-exposure reduction, and continuous wireless monitoring on top of that foundation. WPA3 is an important control within this pattern, but it is not the pattern itself. The result is a reusable, achievable design for organizations that must secure legacy and modern wireless IoT devices at the same time without waiting for a fleet-wide hardware refresh that may never come.
…………………………………………………………………………………………………………………………………………………………………..
References
- Cloud Security Alliance, Zero Trust Guidance for IoT https://cloudsecurityalliance.org/artifacts/zero-trust-guidance-for-iot
- IEEE Std 802.11-2024 (WLAN MAC and PHY base standard) https://standards.ieee.org/ieee/802.11/10548/
- Wi-Fi Alliance WPA3 certification documentation (SAE, Protected Management Frames)
- J. Shelby, “Zero Trust for Multi-RAT IoT: Trust Boundary Management in Heterogeneous Wireless Network Environments,” arXiv:2602.08989
- Rose, S., Borchert, O., Mitchell, S., and Connelly, S., Zero Trust Architecture, NIST Special Publication 800-207, National Institute of Standards and Technology, August 2020.
- https://www.cwnp.com/uploads/1660_cwnp-wp_revisiting-wpa-2-understanding-its-security-gaps-and-evaluating-the-move-to-wpa3_ver120224.pdf
About the author:
Iftikhar Javed khan is an enterprise security architect specializing in wireless security and zero-trust architecture for IoT and critical-infrastructure environments. He holds the Cisco CCIE and CWNP CWNE credentials and is a Senior Member of the IEEE. https://www.linkedin.com/in/iftikhar-j-03aa5533/
SHIELD-6G with AI-native cyber threat intelligence platform to enhance cybersecurity for Europe’s future 6G networks
The SHIELD-6G (Scalable, Hybrid, and Intelligent End-to-End Defense for 6G Networks) project is exploring ways of strengthening cybersecurity for Europe’s future 6G networks. Backed by an €8 million ($9 million) grant from the European Commission, the 36-month initiative brings together 19 international partners to build an AI-native cyber threat intelligence platform for future networks. Telefónica, Ericsson and Nokia are among 19 companies and research organizations from 10 European countries (Ireland, Spain, Finland, France, the Netherlands, Italy, Greece, Latvia, Estonia, and Turkey) are involved. The project is being coordinated by University College Dublin.
“Future 6G networks are expected to support highly sensitive and mission-critical applications, including connected healthcare, autonomous industrial operations, smart manufacturing, maritime connectivity, and resilient public and private communications,” states the press release.
“6G networks will form the foundation of Europe’s next generation of digital services, but their success will depend on trust, resilience, and security by design,” said Madhusanka Liyanage, Associate Professor/Ad Astra Fellow and Director of Graduate Research at the School of Computer Science, University College Dublin, Ireland. “SHIELD‑6G brings together a strong European consortium to develop intelligent cybersecurity capabilities that can protect critical services and support Europe’s digital sovereignty.”
“6G is way more complex than 5G, because it manages more devices, and there’s more automation, and with automation there come problems,” says Bart Siniarski, director at MBP Network Technology, a Shield-6G member organization. “The attack surface will be extended by a couple of magnitudes. So when we step into 6G — which is, to me, 5G on AI steroids — there are going to be problems at the beginning. And then over time [the goal is that] we are comfortable using 6G in critical infrastructure like hospitals or factories or maybe in shipping and militaries.”
………………………………………………………………………………………………………………………………………………………
The SHIELD-6G project tests and validates its AI-native cyber threat intelligence platform across three primary mission-critical use cases. These scenarios are selected because they require ultra-reliable low latency, mass automation, and high security.
Core AI Security Technologies:
Privacy-Preserving Analytics: Uses federated learning and differential privacy to train threat detection models locally on edge devices. Networks share intelligence without exposing sensitive underlying user data.
Explainable AI (XAI): Ensures complex model decisions are transparent by providing clear, human-readable explanations for network blocks or flags. This prevents false alarms from interrupting critical infrastructure like hospitals or shipping lanes.
Zero-Touch Security Orchestration: Combines automation with secure multi-party computation to isolate and mitigate zero-day network breaches. Responses trigger dynamically with minimal human intervention.
Digital Twin Simulation: Embeds AI models into a network digital twin environment to safely stress-test defenses. The software predicts how an attack will propagate before it affects live network traffic.
………………………………………………………………………………………………………………………………………………………
-
- AI-Native Threat Detection: Developing an automated, real-time cyber defense platform for identifying and mitigating known and unknown threats, including zero-day attacks.
- Privacy & Resilience: Using secure multi-party computation and federated learning to ensure user data remains private while improving systemic network resilience.
- Real-World Validation: Testing the 6G security framework across critical use cases such as connected healthcare, smart manufacturing, and maritime connectivity.
- Coordinating Institution: University College Dublin (UCD).
- Key Partners: Includes multinational companies, specialist SMEs (such as UCD spinout MBP Systems), and the global defense and aerospace giant Thales.
- Funding: Backed by the EU under the Horizon Europe program through the Smart Networks and Services Joint Undertaking (SNS JU).
-
- Remote Medical Operations: Securing ultra-low latency connections required for real-time remote robotic surgeries and critical patient monitoring.
- Data Privacy Compliance: Ensuring that highly sensitive personal health telemetry data remains private during processing.
- Interconnected Medical Devices: Safeguarding thousands of continuous-monitoring hospital IoT devices from unauthorized network penetration.
-
- Autonomous Industrial Operations: Protecting automated, closed-loop machinery and collaborative factory floor robots from data injection or remote hijacking.
- Digital Twin Environments: Modeling and simulating cyberattacks safely inside factory digital twins without disrupting ongoing physical production.
- Supply Chain Automation: Securing end-to-end logistics automation against zero-day vulnerabilities in multi-stakeholder industrial software.
- Autonomous Shipping & Logistics: Defending open-sea navigation, automated port loading systems, and vehicle-to-infrastructure communication channels.
- Critical Coastal Infrastructure: Ensuring stable, tamper-proof communications for offshore installations like deep-sea cargo networks and renewable energy hubs.
- Satellite-Terrestrial Handover: Securing the handoff of tracking data as vessels transition between ground stations and global satellite communication networks.
The SHIELD-6G platform utilizes AI-native, privacy-preserving, and automated technologies to establish a Cyber Threat Intelligence (CTI) pipeline tailored for 6G networks. These technologies allow multi-stakeholder networks to self-heal against cascading vulnerabilities without sharing raw data.
……………………………………………………………………………………………………………………………………………………………
References:
https://www.telecoms.com/5g-6g/european-consortium-launches-shield-6g-security-project
https://www.darkreading.com/cybersecurity-operations/eu-6g-network-security
linkedin.com/posts/bartsiniarski_shield6g-6g-cybersecurity-activity-7467489224217460736-A0yi
Analysis & Implications of the Communications Cybersecurity Information Sharing and Analysis Center (C2 ISAC)
Key Differences Between Network Cybersecurity and Control System Cybersecurity & Why It Matters
Anthropic’s Project Glasswing aims to reshape IT cybersecurity
Emerging Cybersecurity Risks in Modern Manufacturing Factory Networks
Cisco to lay off more than 4,000 as it shifts focus to AI and Cybersecurity
StrandConsult Analysis: European Commission second 5G Cybersecurity Toolbox report
GSA Meetup: Cyber Security Continues as Major Obstacle for IoT Adoption
Demythifying Cyber security: IEEE ComSocSCV April 19th Meeting Summary
Analysis & Implications of the Communications Cybersecurity Information Sharing and Analysis Center (C2 ISAC)
The Communications Cybersecurity Information Sharing and Analysis Center (C2 ISAC), announced today, is a private sector-only nonprofit dedicated to strengthening defenses across the U.S. telecommunications industry. The founding members of C2 ISAC are: AT&T, Charter Communications, Comcast, Cox Communications, Lumen Technologies, T-Mobile, Verizon, and Zayo. The board of the nonprofit organization will comprise the chief information and security officers from each of the eight network operators, led by AT&T CISO Rich Baich as chairman. “Cybersecurity threats are more sophisticated and persistent than ever,” Baich said.
The coalition represents a strategic imperative for major network operators to build a unified, rapid-response network to counter sophisticated, AI-driven infrastructure attacks and state-sponsored espionage. It is a meaningful structural change in how the U.S. telecom sector approaches cybersecurity—especially under pressure from increasingly coordinated, AI-enabled threats and nation-state activity.
Traditional ISACs (Information Sharing and Analysis Centers) already exist across sectors—financial services, energy, healthcare—but telecom has historically been more fragmented in how it shares threat intelligence. Operators often guarded incident data due to regulatory exposure, reputational risk, and competitive sensitivities.
C2 ISAC stands out because it is explicitly private-sector-led, rather than government-anchored or compliance-driven. It focuses on telecom infrastructure itself (RAN, core, transport, signaling systems), not just enterprise IT and aims for real-time operational coordination, not just periodic intelligence reports.
“We’re not going to be operating in silos when a potential event occurs. There’ll be information sharing across all that…[and] coordinated response based on that information sharing,” said Baich. “We could be sharing vulnerabilities that we find to be an issue. We could be sharing information related to different types of cyber techniques that are being utilized. Most importantly, though, it is having that trusted forum and the right relationships that someone can just make a phone call to get an answer,” he added.


In effect, it’s closer to a joint cyber defense grid for carriers than a passive information-sharing forum. Several converging pressures explain why this is happening now:
-
AI-enhanced attack capabilities: Adversaries are using AI for automated vulnerability discovery, polymorphic malware, and adaptive intrusion techniques targeting network infrastructure (e.g., signaling exploitation, orchestration layers, and cloud-native cores).
-
State-sponsored campaigns: Groups linked to China, Russia, Iran, and DPRK have increasingly targeted telecom networks for espionage, lawful intercept bypass, metadata harvesting, and potential pre-positioning for disruption.
-
Soft targets in telecom evolution: The shift to:
-
Virtualized RAN (vRAN)
-
Open RAN (multi-vendor complexity)
-
Cloud-native 5G cores
has expanded the attack surface dramatically, especially at APIs, orchestration layers, and inter-vendor interfaces.
-
-
Regulatory pressure without operational mechanisms: Governments (e.g., via CISA, FCC, NSA advisories) have been urging collaboration, but lacked a low-friction, operator-driven mechanism for tactical data exchange.
Key C2 ISAC functions include:
-
Real-time threat intelligence sharing
-
Indicators of compromise (IOCs)
-
Tactics, techniques, and procedures (TTPs)
-
Zero-day exploitation patterns in telecom-specific protocols (e.g., SS7, Diameter, 5G SBA interfaces)
-
-
Coordinated incident response
-
Rapid cross-operator alerts when an intrusion is detected
-
Shared mitigation playbooks (e.g., blocking malicious signaling traffic patterns)
-
Potential “collective defense” actions, like synchronized filtering or patch prioritization
-
-
Infrastructure-specific vulnerability tracking
-
Vendor equipment vulnerabilities (RAN, core, routers, optical transport)
-
Software supply chain risks (containers, orchestration stacks like Kubernetes in 5G cores)
-
-
Simulation and preparedness
-
Joint exercises for large-scale outages or cyber-physical attacks
-
Red-teaming of inter-operator dependencies (e.g., roaming, interconnect)
-
Why this matters strategically:
This is less about incremental improvement and more about closing a structural asymmetry:
-
Attackers collaborate and reuse tooling globally
-
Defenders (telecom operators) have historically operated in silos
C2 ISAC is an attempt to match attacker coordination with defender coordination, particularly in a sector that underpins:
-
National security communications
-
Critical infrastructure interconnectivity
-
Emergency services
-
Financial transaction networks
In that sense, telecom is closer to energy than to typical enterprise IT—and requires a sector-wide defense posture, not just firm-level security.
Implications for the telecom ecosystem:
-
Operators: Likely to gain faster detection and response capabilities, but must overcome internal legal/compliance barriers to share sensitive data.
-
Vendors (e.g., Ericsson, Nokia, Cisco): May face stronger pressure for rapid disclosure and coordinated patching, especially if vulnerabilities affect multiple operators simultaneously.
-
Cloud providers (AWS, Azure, Google Cloud): Become indirectly implicated, since 5G cores and network functions increasingly run on hyperscaler infrastructure.
-
Government: Even though this is private-sector-led, agencies like CISA and NSA will likely act as intelligence feeders and backstops, not primary coordinators.
Risks and limitations:
-
Trust barriers: Operators must be willing to share sensitive breach data quickly—historically a weak point.
-
Legal liability concerns: Information sharing can expose firms to regulatory or litigation risk unless protected.
-
Speed vs. accuracy trade-offs: Real-time sharing increases the risk of false positives propagating across networks.
-
Vendor opacity: If equipment/software vendors are slow or incomplete in disclosures, the ISAC’s effectiveness is constrained.
A useful analogy:
C2 ISAC aims to move telecom from a model of independent air traffic control towers to a shared radar network:
Each network operator still controls its own “airspace,” but now they can all see incoming threats earlier and coordinate responses before collisions—or attacks—propagate system-wide.
References:
https://www.lightreading.com/security/eight-big-us-telcos-join-forces-on-network-cybersecurity
Key Differences Between Network Cybersecurity and Control System Cybersecurity & Why It Matters
Cybersecurity threats in telecoms require protection of network infrastructure and availability
WSJ: T-Mobile hacked by cyber-espionage group linked to Chinese Intelligence agency
GSA Meetup: Cyber Security Continues as Major Obstacle for IoT Adoption
Demythifying Cyber security: IEEE ComSocSCV April 19th Meeting Summary
Key Differences Between Network Cybersecurity and Control System Cybersecurity & Why It Matters
By Joe Weiss with Alan J Weissberger
Introduction:
The Operational Technology (OT) [1.] cybersecurity [2.] community continues to ignore control system cyber-incidents [3.] – a governance failure masquerading as a vocabulary issue.
IT and OT network data breaches are documented in multiple sources such as the Verizon Data Breach Report, CISA documents, and others. Palo Alto Networks notes that nearly 70% of industrial firms had an OT cyber-attack last year. Those cyber-attacks were from data breaches – not always causing equipment damage.
Industrial organizations need an integrated and cyber resilient IT-OT framework to address this increasingly sophisticated threat landscape, but it appears they’re not well prepared to defend against network or control system cyberattacks.
Note 1. Operational Technology refers to the combination of hardware and software designed to directly monitor, control, and manage physical devices, industrial equipment, and critical processes.
Note 2. Cybersecurity can be defined as the practice of protecting people, systems and data from cyberattacks by using various technologies, processes and policies.
Note 3. Cyber-incidents are defined as electronic communications between systems that effects Confidentiality, Integrity, or Availability. This is an IT-centric definition because Safety is not addressed.
Image Credit: txOne Networks
There are two communities addressing cybersecurity:
- The more prevalent community is the one involved in data security. This includes IT and OT network security and is focused on data breaches.
- The second community is focused on engineering security. It is less well-known, but very critical. This discipline is focused on safety, reliability, and productivity.
Professor Ross Anderson stated in his seminal book, “Security Engineering: A Guide to Building Dependable Distributed Systems,” that security engineering is about building systems to remain dependable in the face of malice, error, or mischance.”
The culture gap between network security and engineering organizations will be addressed in the June 2026 issue of IEEE Computer magazine, “Packets and Process: What Network Security and Engineering Get Wrong About Each Other.”
Discussion:
The OT cybersecurity community’s mission is to focus on OT network cyber-attacks. However, its charter does not extend to malicious and unintentional control system cyber incidents involving process sensors, actuators, motors, turbines, transformers, etc.
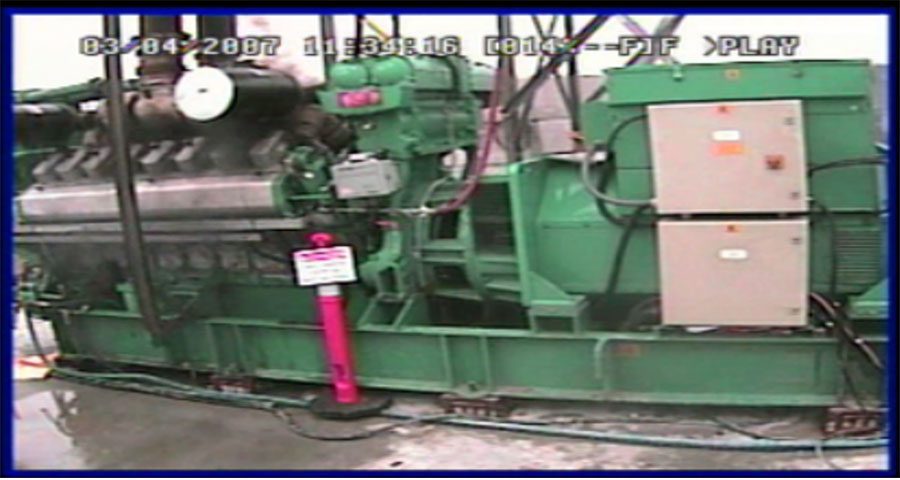
Importantly, control system cyber incidents can be physics-related rather than network-related. The 2007 Aurora vulnerability test at the Idaho National Laboratory destroyed a 2 MW commercial diesel generator by remotely restarting the generator out- of-phase with the grid. This is a gap in protection of the electric grid and was addressed in the October 2025 IEEE Computer magazine article, “Physics-Based Cyberattacks Against Electric Power Grids and Alternating Current Equipment.”
Idaho National Laboratory ran the Aurora Generator Test in 2007 to demonstrate how a cyberattack could destroy physical components of the electric grid. The diesel generator used in the experiment beginning to smoke as shown below:
Aurora Generator Test. Image Credit: Wikipedia
Industry and government OT cybersecurity experts continue to downplay the threat of control system cyberattacks and ignore actual control system incidents that do not originate from OT networks by not calling them cyber-related.
There have been more than 20 million control system cyber incidents that have killed more than 30,000 people. Most of these incidents occurred below the IP-Ethernet layers where there is no cyber forensics nor cybersecurity training. As a result, the majority of these incidents were not identified as being cyber-related.
This indicates that control system cyber incidents that are not classified as IP-Ethernet incidents need their own classification as issues to be addressed by cybersecurity policy, especially for critical infrastructure where accidental and/or malicious cyber failures could result in widespread death and destruction.
Given the current geopolitical environment, nation-states are actively reassessing their capabilities to disrupt adversary infrastructure at scale. In this context, dismissing control system cyber incidents solely because they do not originate from traditional IP-based vectors introduces significant risk. Threat actors are increasingly targeting critical infrastructure and associated control systems—spanning both IT and OT domains—leveraging diverse attack surfaces beyond conventional network entry points.
A parallel issue within both the IT and OT security communities is the tendency to classify incidents as “cyber” only when malicious intent is confirmed. This narrow definition is problematic.
For example, the July 2024 CrowdStrike-related outage, which caused global operational disruptions, clearly met the functional criteria of a cyber-incident due to its systemic impact on networked systems. However, its non-malicious origin led some security governance bodies to exclude it from cyber incident classification. Such distinctions can undermine resilience planning, as they fail to account for the full spectrum of cyber-induced operational risk, including software supply chain failures and systemic misconfigurations.
ERPI Focus:
The European Risk Policy Institute (ERPI) was founded by the Australian Risk Policy Institute as part of the Global Risk Policy Network. EPRI Chairman wrote in a blog titled, “Control system cyber incidents and network breaches are apples and oranges”:
“From our ERPI / 3°C World SRP® perspective, Weiss is pointing at a governance failure masquerading as a vocabulary issue: if you define “cyber incident” through an IT breach lens, you will miss (or dismiss) the incidents that actually move risk —those that degrade continuity lifelines by disrupting physical processes. He makes the case that control-system cyber incidents include electronic/automation failures across sensor signals, control logic, firmware and field device communications, and that many are non-malicious yet still produce loss of view, loss of control, equipment damage, and safety/environmental consequences.
What matters strategically is the reporting and response architecture. Breach-centric metrics (and the cultural reflex that “no attack = no incident”) bias organizations toward under-detection, weak root-cause discipline, and false trend comparisons—exactly when coupled infrastructures are most fragile and repair cycles are tight. Weiss’s bridge condition is practical: align engineering and security on a shared incident definition, and train both communities in control-system incident reality so that operational anomalies are treated as cyber-relevant signals, not “maintenance noise.”
If you’re responsible for critical infrastructure, this is a reminder to recalibrate your incident taxonomy and your board narrative: the control-room outcome is the headline, and the network story is only one possible path to it.”
The Crucial Importance of Process Sensors:
Process sensors represent the biggest gap between data security and engineering security. Perplexity.ai explains this gap in detail -see below, but first we distinguish between data security and engineering security:
- Data security focuses on IP-native devices such as firewalls, routers, switches, etc.
- Engineering security should be focused on engineering devices and equipment that could cause equipment damage and deaths but have no cybersecurity, authentication, or cyber forensics. This includes process sensors, actuators, motors, transformers, inverters, etc. However, that focus is often not achieved.
Perplexity.ai on the Data vs. Information Security Gap:
Process sensors sit at the junction of physical process integrity and digital telemetry, so they expose a gap that neither data security teams nor engineering security teams fully own today. In practice, security teams tend to focus on protecting data pipelines, identities, and networks, while engineering teams focus on measurement accuracy, calibration, availability, and safety; the sensor itself often falls between those disciplines.
Process sensors are not just data endpoints; they are safety- and control-relevant instruments whose outputs can drive operators, PLCs, DCS logic, and downstream automation. If a sensor is spoofed, degraded, miscalibrated, or manipulated, the result is not only bad data but potentially unsafe or physically damaging control actions.
Traditional data security assumes the main problem is confidentiality, integrity, and availability of information in transit or at rest. But process sensors often use legacy field protocols, serial links, gateways, or embedded devices that were engineered for function and reliability rather than cryptographic assurance, making them difficult to secure using conventional enterprise controls.
Engineering security is usually optimized for process correctness, alarms, redundancy, and fail-safe behavior, not adversarial manipulation of the measurement layer. That means the sensor may be treated as trustworthy instrumentation, even though compromised or false sensor data can undermine control logic, operator decisions, and safety systems.
The core mismatch: The real issue is that data security protects the pipeline, while engineering security protects the process, but process sensors belong to both domains. Because ownership is split, sensor trust, authentication, anomaly detection, and physical tamper resistance are often addressed inconsistently or not at all, creating a blind spot at the boundary between cyber and physical risk.
Highlights of Sensors Converge Conference Presentation:
To address these important issues and gaps, I will be presenting at the Sensors Converge conference in Santa Clara, CA on May 7, 2026. The title of my talk is, “Process Sensor Monitoring for Cybersecurity, Reliability, and Safety.” The presentation will include the following topics:
- Process sensors (Level 0 devices) are inherently cyber vulnerable yet remain largely unrecognized by cybersecurity organizations.
- Process sensor incidents, both malicious and unintentional, have caused catastrophic and fatal cyber/operational events across multiple sectors, but were not identified as being cyber-related.
- Fatalities have occurred in every decade since the 1980s, including this decade.
- Monitoring process sensors at the physics level can materially improve reliability, safety, and cybersecurity.
- A discussion of what a process sensor cybersecurity program should include and what organizations should be involved.
- The implications of process sensors which are not cyber-secure, because they don’t meet U.S. and/or EU cybersecurity requirements.
Nation-state actors, including Russia, China, and Iran, understand Level 0 cyber deficiencies. In sharp contrast, most cyber defenders do not and won’t identify process sensor incidents as being cyber-related. This gap helps explain why process sensor cybersecurity remains largely absent from OT security forums and RSA Conference discussions. It may also explain why government OT cybersecurity advisories don’t include insecure Level 0 devices, even though process sensors provide the trusted input to controllers and SCADA/DCS systems.
Conclusions:
Network cybersecurity functions across IT and OT domains, and control system engineering organizations, operate with fundamentally different objectives, taxonomies, and thresholds for identifying and classifying cyber incidents. This divergence has led to a persistent disconnect in how incidents affecting control systems are recognized and addressed within broader network security governance frameworks. Dismissing control system cyber events because they fall outside narrow, IT-centric definitions is not merely a semantic issue—it reflects a structural governance gap with direct implications for critical infrastructure resilience.
To address this, industry and government stakeholders must converge on a harmonized definition of cyber incidents that encompasses both network-centric and control system–centric perspectives. This alignment should be supported by cross-domain training, ensuring that both network security practitioners and engineering teams possess sufficient understanding of control system architectures, threat models, and failure modes. Without such integration, efforts to compare incident frequency, severity, and systemic impact across IT networks and control systems will remain inconsistent and misleading. More critically, this fragmentation will continue to obscure systemic risk, leaving essential infrastructure sectors exposed to increasingly sophisticated and multi-domain cyber threats.
About Joe Weiss:
Joe Weiss is an expert on control system cyber security. He authored the 2010 book, “Protecting Industrial Control Systems from Electronic Threats.”
Joe is an ISA Fellow, Emeritus Managing Director of ISA99, an IEEE Senior Member, has patents on instrumentation, control systems, and OT networks. He is a professional engineer with CISM and CRISC certifications and is a member of Control Process Automation Hall of Fame.
References:
https://www.paloaltonetworks.com/resources/research/state-of-ot-security-report
OT Cybersecurity: The Guide to Securing Industrial Systems
Verizon Business sees escalating risks in mobile and IoT security
Anthropic’s Project Glasswing aims to reshape IT cybersecurity
Emerging Cybersecurity Risks in Modern Manufacturing Factory Networks
Cybersecurity threats in telecoms require protection of network infrastructure and availability
StrandConsult Analysis: European Commission second 5G Cybersecurity Toolbox report
IEEE/SCU SoE Virtual Event: May 26, 2022- Critical Cybersecurity Issues for Cellular Networks (3G/4G, 5G), IoT, and Cloud Resident Data Centers
Cisco CEO sees great potential in AI data center connectivity, silicon, optics, and optical systems
It’s no surprise to IEEE Techblog readers that Cisco’s networking business – still its biggest unit, generating nearly half its total sales – reported <$6.9 billion in revenue for the three-month period ending in January (Cisco’s second fiscal quarter). That was down 3% compared with the same quarter the year before. For its first half year, networking sales dropped 14% year-over-year, to about $13.6 billion.
However, total second-quarter revenues grew 9% year-over-year, to just less than $14 billion, boosted by the Splunk (security company) acquisition in March 2024. Thanks to that deal, Cisco’s security revenues more than doubled for the first half, to about $4.1 billion. But net income fell 8%, to roughly $2.4 billion, due partly to higher costs for research and development, as well as sales and marketing expenses.
Cisco groused about an “inventory correction” as networking customers digested stock they had already bought, but that surely is not the case now as that inventory has been worked off by its customers (ISPs, telcos, enterprise & government end users). Cisco CFO Richard Scott Herren now says “The demand that we’re seeing today a function of extended lead times like we saw a couple of years ago. That’s not the case. Our lead times are not extending.”
Currently, Cisco firmly believes that Ethernet connectivity sales to owners of AI data centers is an “emerging opportunity.” That refers to Cisco’s data center switching solutions for “web-scale” and enterprise customer intra-data center communications. The company’s AI strategy is described here.

Image Courtesy of Cisco Systems
………………………………………………………………………………………………………………………………………
AI investments “will lead to our networking equipment being combined with Nvidia GPUs, and that’s how we’ll accomplish that in the future,” CEO Chuck Robbins told industry analysts on a call to discuss second-quarter results, according to a Motley Fool transcript. “There’s so much change going on right now from a technology perspective that there’s both excitement about the opportunity, and candidly, there’s a little bit of fear of slowing down too much and letting your competition get too much ahead of you. So, we saw solid demand,” he said.
However, Cisco will face mighty competition in that space.
- Nokia is targeting the same opportunity and last month said it would spend an additional €100 million (US$104 million) on its Internet Protocol unit annually with the goal of generating another €1 billion ($1.04 billion) in data center revenues by 2028.
- Arista Networks is another rival in this market, selling high performance Ethernet switches to cloud service providers like Microsoft.
- Nvidia, whose $7 billion acquisition of Mellanox in 2019 gave it effective control of InfiniBand, an alternative to Ethernet that had represented the main option for connecting GPU clusters when analysts published research on the topic in August 2023. Just as important, the Mellanox division of Nvidia also is a leader in Ethernet connectivity within data centers as described in this IEEE Techblog post.
- Juniper Networks (being acquired by HPC) is also focusing on networking the AI data center as per a white paper you can download after filling out this form.
During the Q & A, Robbins elaborated: “On the $700 million in AI orders, it’s a combination of systems, silicon, optics, and optical systems. And I think if you break it down, it’s about half is in silicon and systems. And it continues to accelerate. And I’d say the teams have done a great job on the silicon front. We’ve invested heavily in more resources there. The team is running parallel development efforts for multiple chips that are staggered in their time frames. They’ve worked hard. They were increasing the yield, which is a positive thing. And so, we feel good about it, but it’s a combination of all those things that we’re selling to the customers.”
…………………………………………………………………………………………………………………………………………………………………………………………
Enterprise AI:
“What we’re seeing on the enterprise side relative to AI is it’s still — customers are still in the very early days, and they all realize they need to figure out exactly what their use cases are. We’re starting to see some spending though on specific AI-driven infrastructure. And we think as we get AI pods out there — we got Hyperfabric coming. We got AI defense coming.
We have Hypershield in the market. And we got this new DPU switch, they are all going to be a part of the infrastructure to support these AI applications. So, we’re beginning to see it happen, but I think it’s also really important to understand that as the enterprises leverage their private data, their proprietary data, and they’ll do some training on that and then they’ll run inference obviously against that. We believe that opportunity is an order of magnitude higher than what we’ve seen in training today. We’re going to continue to innovate and build capabilities to put ourselves in a better position to be a real beneficiary as this continues to accelerate. But as of today, we feel like we’re in pretty good shape.”
“If you look at AI defense with the AI Summit that we did recently, there’s — I think there’s about 20-some-odd customers who are interested in going to proof of concept with us right now on it. We had almost half the Fortune 100 there for that event. So, I feel good about where we are. It will turn into greater demand as we just continue to scale these products.”
Telco use of AI Edge Applications:
“We see some of the European network operators are looking at delivering AI as a service,” said Robbins. “We see a lot of them planning for AI edge applications that are sitting at the edge of their networks that they’re managing for customers.”
,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,………………………………………………
Cisco raised its guidance and now expects revenues for the full year of between $56 billion and $56.5 billion, up from its earlier range of $55.3 billion to $56.3 billion.
,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,,………………………………………………
References:
https://www.cisco.com/site/uk/en/solutions/artificial-intelligence/index.html
https://www.juniper.net/content/dam/www/assets/white-papers/us/en/networking-the-ai-data-center.pdf
Nokia selects Intel’s Justin Hotard as new CEO to increase growth in IP networking and data center connections
Initiatives and Analysis: Nokia focuses on data centers as its top growth market
Nvidia enters Data Center Ethernet market with its Spectrum-X networking platform
Aftermath of Salt Typhoon cyberattack: How to secure U.S. telecom networks?
Salt Typhoon Attack: On December 4, 2024, a top U.S. security agency representative confirmed reports that foreign actors, state-sponsored by the People’s Republic of China, infiltrated at least eight U.S. communications companies, compromising sensitive systems and exposing vulnerabilities in critical telecommunications infrastructure. This was part of a massive espionage campaign that has affected dozens of countries. Salt Typhoon has targeted telcos in dozens of countries for upward of two years, officials added.
Dated legacy network equipment and years of mergers and acquisitions are likely impeding the ability of telecommunications providers to prevent China inspired cyber-attacks. Until telecom operators fully secure their networks, China will keep finding ways to come back in, officials have warned.
- On Thursday, FCC chair Jessica Rosenworcel proposed a new annual certification requirement for telecom companies to prove they have an up-to-date cybersecurity risk management plan. More below.
- Senior Cybersecurity and Infrastructure Security Agency and FBI officials confirmed Tuesday that U.S. telcos are still struggling to keep the China-backed hackers out of their networks — and they have no timeline for when total eviction is possible.
FCC Chair Jessica Rosenworcel suggested ‘telecom carriers’ raise their network security methods and procedures: “The cybersecurity of our nation’s communications critical infrastructure is essential to promoting national security, public safety, and economic security,” said Rosenworcel. “As technology continues to advance, so does the capabilities of adversaries, which means the U.S. must adapt and reinforce our defenses. “While the Commission’s counterparts in the intelligence community are determining the scope and impact of the Salt Typhoon attack, we need to put in place a modern framework to help companies secure their networks and better prevent and respond to cyberattacks in the future.”
Rosenworcel’s plan is to make U.S. telcos submit some kind of annual certification to the FCC, proving their cybersecurity measures are up to scratch. The clear inference from the attack itself and all the subsequent attempts to shut the stable door after the horse has bolted is that those efforts currently fall short of the mark. Understandably, none of the specific deficiencies have been publicly detailed.
These proposed FCC measures have been made available to the five members of the Commission. They may choose to vote on them at any moment. If adopted, the Declaratory Ruling would take effect immediately. The Notice of Proposed Rulemaking, if adopted, would open for public comment the cybersecurity compliance framework, which is part of a broader effort to secure the nation’s communications infrastructure.
The FCC press release refers to a recent WSJ report based on an unpublished briefing from U.S. national security adviser Anne Neuberger, in which she detailed the scale of the Salt Typhoon attack. “The Chinese compromised private companies, exploiting vulnerabilities in their systems as part of a global Chinese campaign that’s affected dozens of countries around the world,” she was quoted as saying.
Illustration: Sarah Grillo/Axios
……………………………………………………………………………………………………………………………
Legacy network equipment and years of acquisitions have made it particularly difficult for telcos to patch every access point on their networks, Cliff Steinhauer, director of information security and engagement at the National Cybersecurity Alliance, told Axios.
- Many of the systems in question are nearly 50 years old — like landline systems — and they were “never meant for the type of sensitive data and reliance that we have on them right now,” he said.
- During an acquisition, a company could also miss a server when taking stock of all its newly acquired equipment, Steinhauer said. Network engineers are often inundated with security alerts that are hard to prioritize, he added.
- U.S. telecommunications carriers are required to provide a way for law enforcement to wiretap calls as needed — providing another entry point for adversaries.
Many of the security problems telcos face require simple fixes, like implementing multifactor authentication or maintaining activity logs.
- Even CISA’s recent guidance for securing networks focuses on the security basics.
- But to keep China out, telcos would have to make sure that every device — including their legacy physical equipment, online servers and employees’ computers — is patched.
Most high-profile cyberattacks across industries come down to the basics: a compute server that didn’t have multifactor authentication turned on or an employee who was tricked into sharing their password. Even if a company invests all of its resources in cybersecurity, it may not be enough to fend off a sophisticated nation-state like China.
- These actors are skilled at covering their tracks: They could delete activity logs, pose as legitimate users, and route their traffic through compromised computers in the U.S. so they aren’t detected.
- “You’ve got a persistent, motivated attacker with vast resources to poke and prod until they get in,” Mr. Steinhauer said.
References:
https://docs.fcc.gov/public/attachments/DOC-408015A1.pdf
https://www.axios.com/2024/12/06/telecom-cybersecurity-china-hack-us
WSJ: T-Mobile hacked by cyber-espionage group linked to Chinese Intelligence agency
WSJ: T-Mobile hacked by cyber-espionage group linked to Chinese Intelligence agency
According to the Wall Street Journal, T-Mobile’s network was hacked in a damaging Chinese cyber-espionage operation that successfully gained entry into multiple U.S. and international telecommunications companies.
Hackers linked to a Chinese intelligence agency were able to breach T-Mobile as part of monthslong campaign to spy on the cellphone communications of high-value intelligence targets. It is unclear what information, if any, was taken about T-Mobile customers’ calls and communications records.
“T-Mobile is closely monitoring this industry-wide attack, and at this time, T-Mobile systems and data have not been impacted in any significant way, and we have no evidence of impacts to customer information,” a company spokeswoman said. “We will continue to monitor this closely, working with industry peers and the relevant authorities.”

China’s multipronged spying operations have drawn warnings in the U.S. about their economic implications. Photo: Andy Wong/Associated Press
…………………………………………………………………………………………………………………………………………………………………………..
Salt Typhoon used sophisticated methods to infiltrate American telecom infrastructure through vulnerabilities including Cisco Systems routers, and investigators suspect the hackers relied on artificial intelligence or machine learning to further their espionage operations , people familiar with the matter said. The attackers penetrated at least some of that infrastructure over eight months or more.
In the broader hacking campaign, attackers were able to access cellphone lines used by an array of senior national security and policy officials across the U.S. government, in addition to politicians. The access allowed them to scoop up call logs, unencrypted texts and some audio from targets, in what investigators believe may have significant national-security ramifications.
Additionally, the hackers were able to access information from systems maintained by the carriers to comply with U.S. surveillance requests, raising further counterintelligence concerns. Investigators are still endeavoring to fully understand and have said the attack was carried out by the Salt Typhoon group. At Lumen, which doesn’t provide wireless service, the attackers didn’t steal any customer data or access its wiretap capabilities, according to people familiar with the matter.
Further investigation has revealed that the hackers sought access to data managed under U.S. law enforcement programs, including those governed by the Foreign Intelligence Surveillance Act (FISA). This act authorizes American intelligence agencies to monitor suspected foreign agents’ communications. By targeting these programs, Chinese hackers may have aimed to infiltrate sensitive government communications channels, gaining insights into U.S. surveillance efforts.
Some foreign telecommunications firms were also compromised in the hacks, including in countries that maintain close intelligence-sharing partnerships with the U.S., people familiar with the matter said. Earlier this week, the Biden administration acknowledged in a public statement some details about the nature of the “broad and significant” hack that were previously reported by the WSJ.
Chinese government-linked hackers had compromised networks at multiple telecommunications companies “to enable the theft of customer call records data, the compromise of private communications of a limited number of individuals who are primarily involved in government or political activity, and the copying of certain information that was subject to U.S. law enforcement requests pursuant to court orders,” the statement from the FBI and Cybersecurity and Infrastructure Security Agency (CISA) said. “We expect our understanding of these compromises to grow as the investigation continues,” they added.
References:
https://www.wsj.com/tech/cybersecurity/u-s-wiretap-systems-targeted-in-china-linked-hack-327fc63b
https://www.newsweek.com/fbi-chinese-cyber-espionage-multiple-telecom-networks-1985617
China backed Volt Typhoon has “pre-positioned” malware to disrupt U.S. critical infrastructure networks “on a scale greater than ever before”
FBI and MI5 Chiefs Issue Joint Warning: Chinese Cyber Espionage on Tech & Telecom Firms
Cybersecurity threats in telecoms require protection of network infrastructure and availability
FT: A global satellite blackout is a real threat; how to counter a cyber-attack?
Demythifying Cyber security: IEEE ComSocSCV April 19th Meeting Summary
StrandConsult Analysis: European Commission second 5G Cybersecurity Toolbox report
Cisco to lay off more than 4,000 as it shifts focus to AI and Cybersecurity
Frontier Communications recovering from unknown cyberattack!
Frontier Communications provides fiber optic based gigabit Internet access to millions of consumers and businesses across 25 states. Frontier Communications said on Thursday that it’s ‘experiencing technical issues with our internal support platforms.’ Frontier’s mobile apps are also down, with the same warning message being displayed after launching the application. A company representative did not respond to questions about the situation.
The Texas-based telecommunications company reported a cyberattack to the Securities and Exchange Commission (SEC) on Thursday. Frontier said it detected unauthorized access to its IT systems on April 14th and began instituting “containment measures” that included “shutting down certain of the Company’s systems.” The shutdowns caused operational disruption that the company said “could be considered material.”
“Based on the Company’s investigation, it has determined that the third party was likely a cybercrime group, which gained access to, among other information, personally identifiable information,” the company said in the SEC filing.
“As of the date of this filing, the Company believes it has contained the incident and has restored its core information technology environment and is in the process of restoring normal business operations. Based on the company’s investigation, it has determined that the third party was likely a cybercrime group, which gained access to, among other information, personally identifiable information,” the company said.
Investigations into the incident are ongoing and they have hired cybersecurity experts to help with the incident. Law enforcement agencies have been notified.
Despite saying that the shutdowns could be considered material, Frontier later wrote that it “does not believe the incident is reasonably likely to materially impact the Company’s financial condition or results of operations.”
According to Leichtman Research Group, Frontier is the seventh largest broadband Internet supplier in the US, with almost 3 million customers. The company’s copper and fiber network stretches across large portions of the East and West Coasts.
Light Reading reported on Thursday of warnings from Frontier. “We’re experiencing technical issues with our internal support platforms,” said a message on the company’s website homepage. “Our residential and business networks are not affected by this issue. In the meantime, please call for assistance.”
……………………………………………………………………………………………………………………………
Last week, AT&T reported that more than 51 million people were affected by a recently-disclosed data breach that included troves of customer information including Social Security numbers, AT&T account numbers and AT&T passcodes.
EchoStar’s Dish Network last year reported a “cybersecurity incident” that impacted its ability to install services, take payments and provide customer care for several weeks.
Fierce reported this week about an intentional cable cut in AT&T’s network that interrupted services at Sacramento Airport.
……………………………………………………………………………………………………………………..
The Federal Communications Commission (FCC) updated its data breach rules for the first time in 16 years in December, expanding regulations on how telecommunication companies report cybersecurity incidents. FCC Chairwoman Jessica Rosenworcel argued that the rules the agency created more than 15 years ago are no longer compatible with a modern world where telecommunication carriers have access to a “treasure trove of data about who we are, where we have traveled, and who we have talked to.”
References:
https://therecord.media/telecom-giant-frontier-cyberattack-sec
https://www.sec.gov/ix?doc=/Archives/edgar/data/20520/000119312524100764/d784189d8k.htm
https://www.lightreading.com/security/frontier-we-were-probably-hacked